The curious case of missing Authorization header
I have been wasting time on a small issue adding Authorization header into HttpClient.
The code was plain and simple:
using (var httpClient = new HttpClient
{
    DefaultRequestHeaders = { Authorization = new AuthenticationHeaderValue("Basic", Convert.ToBase64String(Encoding.ASCII.GetBytes(username + ":" + password)))
})
{
    var response = await httpClient.GetAsync(url);
}
Specifically, I was writing a .NET Core console app, following this wiki page https://github.com/projectkudu/kudu/wiki/Accessing-the-kudu-service and trying to access http://mysite.scm.azurewebsites.net/basicauth. However, I kept getting 401 Unauthorize response and response.RequestMessage.Headers was completely empty.
After having spent some time searching for solution on the Internet but to no avail, I opened Fiddler to see the actual HTTP requests. Turns out, this was what happened behind the scene:
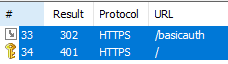
There were actually 2 requests. The first one has the Authorization header and returns a 302 Found. Automatic redirection of HttpClient triggers the second request, and this one didn’t have any Authorization header.
Normally I can just stop there, accept that how things work in .NET and find a workaround. But since .NET Core is open source on GitHub, I decided to dig a bit deeper to understand the reason of this implementation. A quick search about redirection on the corefx repo in GitHub gave me the exact commit that I need: https://github.com/dotnet/corefx/commit/e8a17715fba4ba6cfce4043a2cd117474dfcee05. And voila, I could see the line in RedirectHandler.cs that causing the issue:
request.Headers.Authorization = null;and I could also see the reason in SocketsHttpHandler.cs:
// Just as with WinHttpHandler and CurlHandler, for security reasons, we do not support authentication on redirects
// if the credential is anything other than a CredentialCache.
// We allow credentials in a CredentialCache since they are specifically tied to URIs.
I finally solved my curious case, and I hope this post is useful to you. Feel free to leave me a comment and let me know if you have any suggestion on securely implement the redirection with Authorization header.
Comments
3 comments from the original WordPress blog.
https://stackoverflow.com/questions/28564961/authorization-header-is-lost-on-redirect
Just re-add the Authorization header if you are happy with the post-redirection URL (e.g. it's the same hostname or whatever)
Thanks for the advise. I am just not sure what validation for the URL I would need in this case.
How to add Authorization header in RedirectHandler ?